Training Program · Registration Open
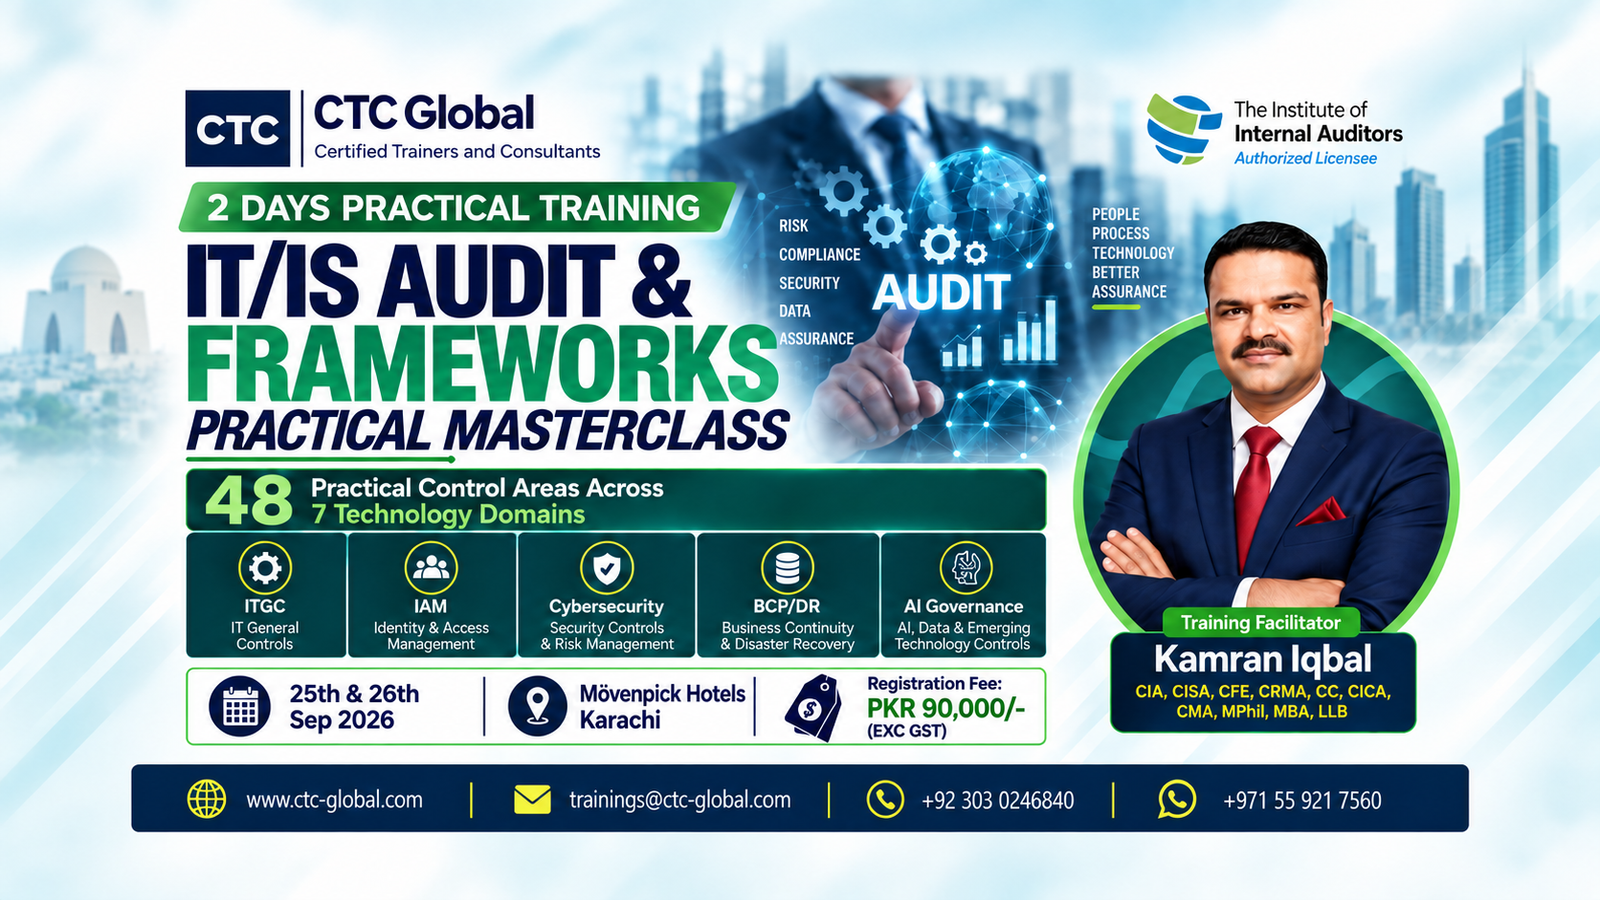
IT/IS Audit & Frameworks Practical Masterclass 2026 (Karachi)
A 2-day practitioner-led masterclass designed to build practical IT/IS audit capability across ITGC, identity and access management, cybersecurity, data and privacy, business continuity, SDLC, vendor controls, AI governance and emerging technology risks.
Date05 Nov 2026
Time9:00 AM PKT
DeliveryPhysical
CPD16.0 Hours
LanguageEnglish
Master IT/IS Audit through 48 practical control areas across 7 critical technology domains.
The IT/IS Audit & Frameworks Practical Masterclass is an intensive, practitioner-led two-day training programme designed to help professionals plan, perform, document and report IT/IS audit assignments with greater confidence and technical depth.
The programme connects recognized IT audit frameworks with real technology risks, control evaluation techniques, audit procedures, evidence requirements and reporting expectations.
Rather than treating IT audit as a purely technical subject, the masterclass focuses on how auditors actually evaluate technology governance and controls in practice. Participants will work through 48 practical control areas across seven major IT risk and technology domains, covering IT General Controls, Identity & Access Management, Cybersecurity, Data, Privacy & Cloud Controls, Business Continuity & Resilience, SDLC/Vendor/Procurement Controls, and AI Governance & Emerging Technology Controls.
A dedicated IT Audit Tool Live Workshop further connects the concepts to practical control assessment, testing procedures, evidence requirements and common audit observations.
Who Should Attend
Chief Audit Executives, Heads of Internal Audit and Heads of IT/IS Audit
Audit Managers, Internal Auditors, IT Auditors and audit team members seeking stronger practical IT/IS audit capability.
IT Managers, Cybersecurity Professionals, Information Security Teams and Technology Control Owners responsible for technology controls.
Risk Managers, Compliance Professionals, Governance Professionals and Control Owners responsible for technology-risk oversight.
Learning Outcomes
Understand the Role of IT/IS Audit
Understand how IT/IS audit supports governance, risk management, assurance and compliance objectives.
Assess IT General Controls
Identify and assess key IT General Controls and application-related technology risks.
Evaluate Core Technology Controls
Evaluate user access, privileged access, change management, IT operations, backup and recovery, and segregation-of-duties controls.
Audit Specialized Technology Areas
Apply audit procedures across cybersecurity, privacy, cloud, BCP/DR, SDLC, vendor management and emerging technologies.
Apply a Structured IT Audit Assessment Approach
Use a structured IT/IS Audit Assessment Tool covering 48 control areas across seven technology domains.
Strengthen IT Audit Reporting
Assess IT audit reports for clarity, accuracy, objectivity, completeness, evidence support and Audit Committee suitability.
Program Agenda
01 — Welcome & Programme Orientation ITAF 5th Edition overview and relevance to IT/IS audit; ISO 27001 context and relationship with practical control assessment
02 — Module 1: IT General Controls (ITGC) User Access Management & Privileged Access Control; Change Management; IT Operations & Availability; Data Backup & Recovery; Segregation of Duties
03 — Module 2: Identity & Access Management (IAM) User provisioning/de-provisioning; MFA; PAM; third-party/vendor access; access reviews; recertification; RBAC
04 — Module 3: Cybersecurity Controls Audit Security governance; network and endpoint security; vulnerability management; SIEM/security monitoring; incident-response controls
05 — IT Audit Tool Live Workshop Practical assessment of controls; application of audit test procedures; evidence requirements; common observations and control gaps
06 — Module 4: Data, Privacy & Cloud Controls Data classification and governance; data quality; database security; retention/disposal; PIA/DPIA; cloud-data and cloud-security controls
07 — Module 5: Business Continuity & Resilience BCP framework; BIA; Disaster Recovery planning; DR testing; IT resilience architecture; crisis communication
08 — Module 6: SDLC, Vendor & Procurement Controls SDLC governance; Security by Design; QA/UAT; production migration controls; vendor and third-party management
09 — Module 7: AI Governance & Emerging Controls AI/algorithm governance; Cloud & SaaS security; SOC monitoring; penetration testing; endpoint/MDM; encryption/key management; DLP; IT financial controls
10 — Closing, Q&A & Certification Practical implementation discussion, key takeaways, participant Q&A and certificate distribution
Kamran Iqbal
Lead Trainer
CIA, CISA, CFE, CRMA, CC, CMA, MBA, MPhil, LLB, FMVA
Kamran Iqbal is an International Trainer, IIA Approved Faculty Member, and seasoned audit and risk professional with 20+ years of experience across internal audit, IT/IS audit, risk management, governance, internal controls, fraud and data analytics.
For more than a decade, he has delivered professional training programmes to professionals and organizations across diverse sectors, with a strong emphasis on practical application rather than purely theoretical learning.
He is also the author of various professional books, audit checklists and practical tools designed for internal audit, risk and assurance professionals.